Small Business CyberSecure
Starter Kit$129
Professional$249
Any business that keeps Floridians' personal information has to protect it and report breaches fast. Here is what the law asks for in plain English, and editable policies to put your security in writing.
Updated October 18, 2026 · Get the free self-assessment
The Florida Information Protection Act (Fla. Stat. §501.171) applies to businesses that acquire, maintain, store or use personal information about Florida residents. That includes things like names combined with Social Security, driver's license or account numbers, medical or health insurance information, and online login credentials.
The core duty is simple: take reasonable measures to protect and secure that data. The law doesn't list specific controls, so written policies are how you show what "reasonable" means at your business.
If there is a breach, you must notify affected individuals no later than 30 days after determining a breach occurred or having reason to believe one did. If 500 or more Floridians are affected, you must also notify the Florida Department of Legal Affairs within 30 days. Vendors that hold data for you must tell you within 10 days.
When you no longer need customer records, you must dispose of them so the information is unreadable, for example by shredding or wiping.
Every document is editable Word or Excel. Items marked Pro are in the Professional Edition only.
| Requirement | What it means for you | Kit documents |
|---|---|---|
| Reasonable measures (§501.171(2)) | A written security program sized to your business. |
|
| Access control and MFA | Protect email, banking and business apps. |
|
| Encryption and data protection | Protect personal information at rest and in transit. |
|
| Staff training | Teach employees to spot phishing and handle data safely. |
|
| Vendors (10-day notice, §501.171(6)) | Vet vendors that hold your data and set notice expectations. |
|
| 30-day breach notice (§501.171(3)-(4)) | A plan to investigate and notify on time. |
|
| Secure disposal (§501.171(8)) | Shred or wipe records you no longer need. |
|
| Backups and continuity | Get back up and running after ransomware or an outage. |
|
| Payment and wire fraud | Verify bank detail changes before you pay. |
|
Plain-language templates with bracketed fields for your details, policy IDs that stay the same when you upgrade, and a footer reminding you to customize before use.
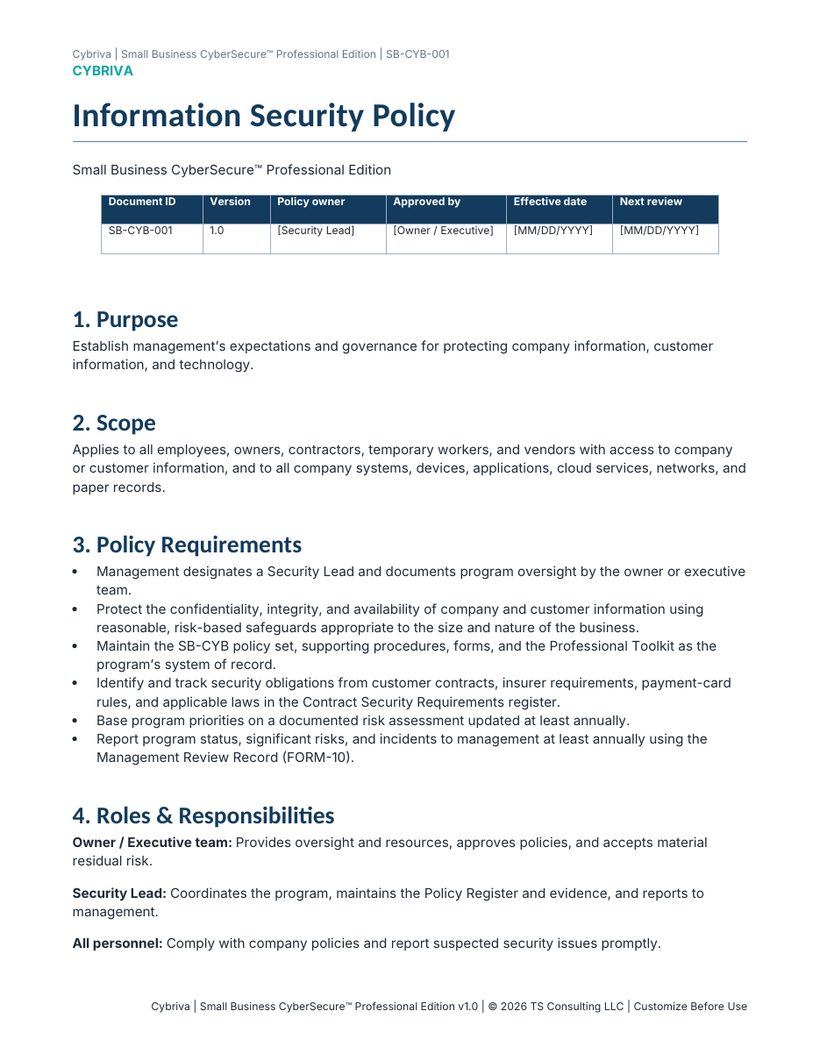
Policy numbers carry over from the Starter Kit to the Professional Edition, so you can start small and upgrade without renumbering.
22 editable files
40 editable files
If your business acquires, maintains, stores or uses personal information about Florida residents, it likely does, regardless of size. Check with counsel for your situation.
Notify affected individuals no later than 30 days after determining a breach occurred or having reason to believe one did. If 500 or more Floridians are affected, notify the Department of Legal Affairs within the same window.
No. It requires reasonable measures. Written policies covering access control, MFA, encryption, training and incident response are a practical way to show what you do.
No. The policies work anywhere, but this guide explains Florida's law. Other states have their own breach and security laws.
No. These are editable templates and education. Have your attorney review documents that carry legal obligations.
Answer 50 yes / no / not sure questions across 10 areas. Score your results and get clear next steps for your industry.
Thanks. Your download should start automatically. If it doesn't, use the button below.
Download the PDFQuestions about your results? Email info@cybriva.ai.
Start with the Starter Kit or get every policy, form and workbook in the Professional Edition. Policy numbers carry over if you upgrade.
See the full Small Business CyberSecure pageThis guide is plain-English education, current as of October 18, 2026. It is not legal advice, an audit or a compliance determination, and Cybriva is not affiliated with any regulator or standards body named here. Rules change and vary by state; confirm how they apply to you with your attorney or compliance advisor.