Insurance data security law template for agencies (NAIC Model Law #668)
Most states now require licensed insurance agencies to run a written information security program. Here is what the NAIC model law asks for in plain English, how to check your state, and editable templates that map to it.
- Plain English
- Editable Word & Excel
- Free self-assessment
Updated October 18, 2026 · Get the free self-assessment
What insurance data security laws require, in plain English
The NAIC Insurance Data Security Model Law (#668) is the template most states use for insurance cybersecurity rules. NAIC's adoption map shows more than 25 jurisdictions with a version in place. It applies to licensees, which includes agencies and producers licensed by the state insurance department.
Under Section 4, a licensee needs a written information security program based on a risk assessment. The program must include safeguards such as access controls, encryption, multi-factor authentication, audit trails, training and an incident response plan, plus oversight of third-party service providers. Safeguards must be reviewed at least annually.
After a cybersecurity event, Section 6 requires notice to the insurance commissioner within 72 hours when the state is your home state, or when the event involves 250 or more of that state's residents and meets the other conditions.
Licensees with fewer than 10 employees (including independent contractors) are exempt from the written program requirement under the model. That exemption does not cover the notice duties. Your state's version may differ.
Where each requirement is covered in the Insurance Agency CyberSecure kit
Every document is editable Word or Excel. Items marked Pro are in the Professional Edition only.
| Requirement | What it means for you | Kit documents |
|---|---|---|
| Written information security program (Sec. 4) | A written program scaled to your agency's size and data. |
|
| Risk assessment | Identify threats, including those from vendors, and review safeguards yearly. |
|
| Access control, MFA and encryption | Protect agency management and carrier portals. |
|
| Training | Train staff and producers on phishing and data handling. |
|
| Third-party service providers | Require vendors to protect nonpublic information. |
|
| Incident response plan | A written plan for cybersecurity events. |
|
| 72-hour commissioner notice (Sec. 6) | Work out who to notify, and by when. |
|
| Retention and disposal | Destroy nonpublic information you no longer need. |
|
| Annual reporting to leadership | Report on the program at least yearly. |
|
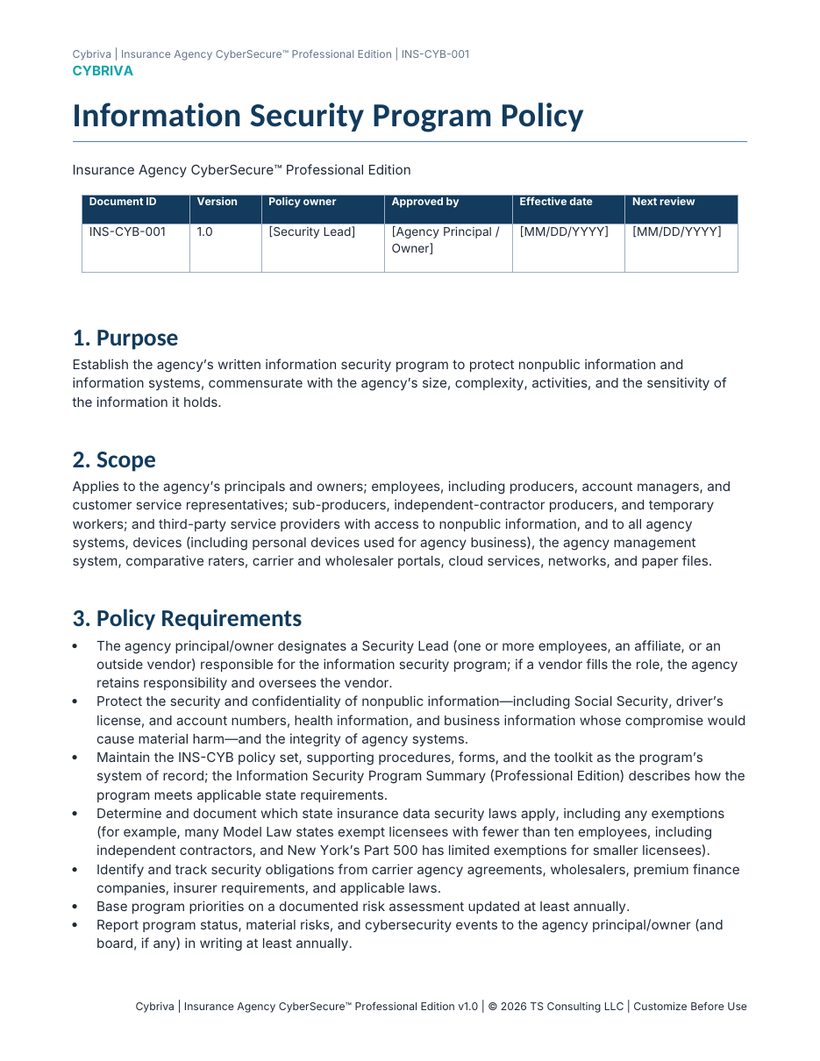
What the Information Security Program Policy looks like
Plain-language templates with bracketed fields for your details, policy IDs that stay the same when you upgrade, and a footer reminding you to customize before use.
- Download right after checkout
- Edit in Microsoft Word, Google Docs or any word processor
- One-time price: Starter $149 · Professional $249
Every file in each edition
Policy numbers carry over from the Starter Kit to the Professional Edition, so you can start small and upgrade without renumbering.
Starter Kit
$14923 editable files
Policies 15
- INS-CYB-001Information Security Program Policy
- INS-CYB-002Cybersecurity Roles & Responsibilities Policy
- INS-CYB-003Risk Assessment Policy
- INS-CYB-004Password & Authentication Policy
- INS-CYB-005Access Control Policy
- INS-CYB-006Multi-Factor Authentication Policy
- INS-CYB-007Acceptable Use Policy
- INS-CYB-008Security Awareness & Training Policy
- INS-CYB-009Email & Phishing Security Policy
- INS-CYB-010Endpoint Security Policy
- INS-CYB-011Mobile & Remote Work Policy
- INS-CYB-012Nonpublic Information Protection & Encryption Policy
- INS-CYB-013Backup & Recovery Policy
- INS-CYB-014Cybersecurity Event Response & Notification Policy
- INS-CYB-015Business Continuity & Disaster Recovery Policy
Plans, guides & assessments 7
- WordImplementation Guide
- WordStaff & Producer Cybersecurity Quick Guide
- WordIncident Response Plan
- WordPolicyholder Payment & Policy Change Advisory
- Word30-60-90 Day Action Plan
- Word50-Point Cybersecurity Checklist
- WordCybersecurity Maturity Assessment
Workbook 1
- ExcelInsurance Agency CyberSecure Toolkit
Professional Edition
$24942 editable files
Policies 21
- INS-CYB-001Information Security Program Policy
- INS-CYB-002Cybersecurity Roles & Responsibilities Policy
- INS-CYB-003Risk Assessment Policy
- INS-CYB-004Password & Authentication Policy
- INS-CYB-005Access Control Policy
- INS-CYB-006Multi-Factor Authentication Policy
- INS-CYB-007Acceptable Use Policy
- INS-CYB-008Security Awareness & Training Policy
- INS-CYB-009Email & Phishing Security Policy
- INS-CYB-010Endpoint Security Policy
- INS-CYB-011Mobile & Remote Work Policy
- INS-CYB-012Nonpublic Information Protection & Encryption Policy
- INS-CYB-013Backup & Recovery Policy
- INS-CYB-014Cybersecurity Event Response & Notification Policy
- INS-CYB-015Business Continuity & Disaster Recovery Policy
- INS-CYB-016Third-Party Service Provider Security Policy
- INS-CYB-017Generative AI Acceptable Use Policy
- INS-CYB-018Vulnerability & Patch Management Policy
- INS-CYB-019Records Retention & Disposal Policy
- INS-CYB-020Payment, Payee & Policy Change Verification Policy
- INS-CYB-021AI Governance Policy
Plans, guides & assessments 10
- WordProfessional Edition Implementation Guide
- WordIncident Response Plan & Playbooks
- WordTabletop Exercise Kit
- Word30-60-90 Day Action Plan
- WordStaff & Producer Cybersecurity Quick Guide
- WordPolicyholder Payment & Policy Change Advisory
- WordInformation Security Program Summary & Applicability Worksheet
- Word50-Point Cybersecurity Checklist
- WordCybersecurity Maturity Assessment
- Word50-Question Insurance Agency Cybersecurity Self-Assessment
Forms & templates 10
- FORM-01Payment, Payee & Policy Change Verification Form
- FORM-02Access Request Form
- FORM-03Staff & Producer Offboarding Checklist
- FORM-04Software & SaaS Request Form
- FORM-05Security Exception Request
- FORM-06Cybersecurity Event Intake Form
- FORM-07Third-Party Service Provider Questionnaire
- FORM-08Policy Acknowledgment Form
- FORM-09Cybersecurity Event Notification Worksheet
- FORM-10Annual Program Report & Management Review
Workbook 1
- ExcelInsurance Agency CyberSecure Professional Toolkit
Frequently asked questions
Has my state adopted the NAIC Insurance Data Security Model Law?
NAIC's map shows more than 25 jurisdictions with a version in place. Florida had not adopted it as of mid-2026. Check NAIC's adoption map and your state insurance department for the current rules.
Are small agencies exempt?
Under the model law, licensees with fewer than 10 employees, including independent contractors, are exempt from the written program requirement. The model's exemption does not cover the notice duties, and each state's version can differ.
How fast do we have to notify the commissioner?
Under the model law, as promptly as possible and no later than 72 hours after determining that a cybersecurity event occurred.
Does the FTC Safeguards Rule apply to insurance agencies?
Generally no. Insurance is regulated by the states, so the data security rules for agencies come from state insurance law and general state breach laws.
Is this legal advice?
No. These are editable templates and education, not a compliance determination.
Free Insurance Agency cybersecurity self-assessment
Answer 50 yes / no / not sure questions across 10 areas. Score your results and get clear next steps for your industry.
- Small Business, Law Office, Real Estate, Healthcare, Accounting & Tax, Insurance Agency, Financial Advisor, Auto Dealer, Mortgage & Title, and Cyber Insurance Readiness editions
- Starred priority questions and a scoring table
- Printable PDF
Your assessment is ready
Thanks. Your download should start automatically. If it doesn't, use the button below.
Download the PDFQuestions about your results? Email info@cybriva.ai.
Get the Insurance Agency CyberSecure kit
Start with the Starter Kit or get every policy, form and workbook in the Professional Edition. Policy numbers carry over if you upgrade.
See the full Insurance Agency CyberSecure pageSources
- NAIC Insurance Data Security Model Law (#668)
- NAIC adoption map for Model #668
- SiaReg: NAIC Model 668 state adoption tracker
- Florida Statutes § 501.171, Security of confidential personal information
This guide is plain-English education, current as of October 18, 2026. It is not legal advice, an audit or a compliance determination, and Cybriva is not affiliated with any regulator or standards body named here. Rules change and vary by state; confirm how they apply to you with your attorney or compliance advisor.