Law Office CyberSecure
Starter Kit$149
Professional$249
Lawyers have an ethical duty to protect client information, respond to breaches and use AI tools carefully. Here is what the ABA guidance says in plain English, and editable policies that put it in writing.
Updated October 18, 2026 · Get the free self-assessment
Model Rule 1.6(c) requires lawyers to make reasonable efforts to prevent unauthorized access to or disclosure of client information. Rule 1.1 (competence, including Comment 8 on technology) and Rules 5.1 and 5.3 (supervising lawyers and staff) extend that duty across the firm.
Formal Opinion 477R (2017) explains what reasonable efforts look like for electronic communications: understand your risks, use appropriate security such as encryption for sensitive matters, train staff and vet vendors.
Formal Opinion 483 (2018) covers what to do after a data breach: monitor for breaches, act reasonably to stop them and restore systems, and tell current clients when their information was or may have been compromised.
Formal Opinion 512 (2024) applies these duties to generative AI. Lawyers must understand the tools they use, protect confidential information put into them, supervise their use and be candid about fees.
Every document is editable Word or Excel. Items marked Pro are in the Professional Edition only.
| Requirement | What it means for you | Kit documents |
|---|---|---|
| Reasonable security (Rule 1.6(c), Op. 477R) | Written security program scaled to your firm and clients. |
|
| Secure communications (Op. 477R) | Encrypt sensitive email and files; secure remote work. |
|
| Access control and MFA | Lock down document management, email and billing systems. |
|
| Supervision and training (Rules 5.1, 5.3) | Train attorneys and staff and get signed acknowledgments. |
|
| Vendor and cloud diligence (Op. 477R) | Vet cloud and IT providers before trusting them with client data. |
|
| Breach response and client notice (Op. 483) | Detect, stop and recover, then evaluate client notice. |
|
| Generative AI (Op. 512) | Rules for which AI tools may be used, and how. |
|
| Trust account and wire security | Verify every wire and payment instruction change. |
|
| File retention | Keep and dispose of client files on a schedule. |
|
Plain-language templates with bracketed fields for your details, policy IDs that stay the same when you upgrade, and a footer reminding you to customize before use.
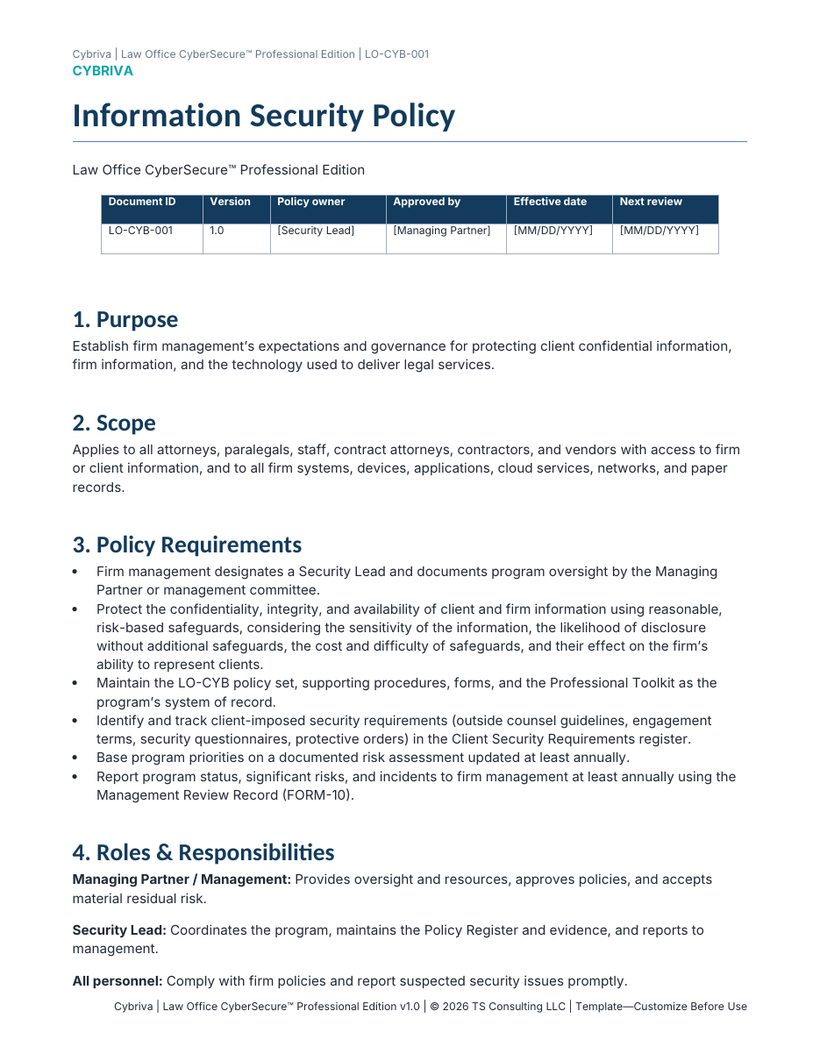
Policy numbers carry over from the Starter Kit to the Professional Edition, so you can start small and upgrade without renumbering.
22 editable files
40 editable files
The Model Rules don't name a specific document, but Rule 1.6(c) requires reasonable efforts to protect client information. A written policy is the clearest way to show what your firm does and to train the people you supervise.
Monitor for breaches, act reasonably and promptly to stop a breach and mitigate the harm, and inform current clients when a breach has compromised, or may have compromised, their confidential information.
Yes. The Professional Edition includes a Generative AI Acceptable Use Policy and an AI Governance Policy that reflect the themes of Formal Opinion 512.
Yes. Your state's rules and ethics opinions control. Check them and adjust the templates.
No. These are editable templates and education. Cybriva is not affiliated with the ABA.
Answer 50 yes / no / not sure questions across 10 areas. Score your results and get clear next steps for your industry.
Thanks. Your download should start automatically. If it doesn't, use the button below.
Download the PDFQuestions about your results? Email info@cybriva.ai.
Start with the Starter Kit or get every policy, form and workbook in the Professional Edition. Policy numbers carry over if you upgrade.
See the full Law Office CyberSecure pageThis guide is plain-English education, current as of October 18, 2026. It is not legal advice, an audit or a compliance determination, and Cybriva is not affiliated with any regulator or standards body named here. Rules change and vary by state; confirm how they apply to you with your attorney or compliance advisor.