Reg S-P incident response program template for small RIAs
Amended Regulation S-P now applies to smaller SEC-registered advisers. Here is what it requires in plain English, and editable templates that map to each piece.
- Plain English
- Editable Word & Excel
- Free self-assessment
Updated October 18, 2026 · Get the free self-assessment
What amended Regulation S-P requires, in plain English
The SEC amended Regulation S-P in 2024. Every covered firm now needs a written incident response program that is reasonably designed to detect, respond to and recover from unauthorized access to or use of customer information. The program must assess what happened, contain and control the incident, and notify affected people.
If sensitive customer information was, or is reasonably likely to have been, accessed or used without authorization, you must notify affected individuals as soon as practicable and no later than 30 days after you become aware of it. You can skip notice only if a reasonable investigation shows substantial harm or inconvenience is not reasonably likely, and you need to document that determination.
You also need written policies to oversee service providers such as custodians, CRMs and IT firms. They must be required to protect customer information and to tell you within 72 hours of becoming aware of a breach in their systems that affects your customers.
Finally, the amendments add recordkeeping requirements for the program, investigations, notice decisions and service provider arrangements.
Where each requirement is covered in the Financial Advisor CyberSecure kit
Every document is editable Word or Excel. Items marked Pro are in the Professional Edition only.
| Requirement | What it means for you | Kit documents |
|---|---|---|
| Written incident response program | A written program to detect, respond to and recover from incidents. |
|
| Assess and contain | Figure out scope and which systems and data were hit, then stop the spread. |
|
| 30-day customer notice | Notify affected individuals unless a documented determination says no harm is likely. |
|
| Service provider oversight and 72-hour notice | Vet providers and require them to notify you within 72 hours. |
|
| Safeguards and disposal | Policies that protect customer records and dispose of them properly. |
|
| Identity theft red flags (Reg S-ID) | A program to spot and respond to identity theft warning signs. |
|
| Recordkeeping and annual review | Keep the written records and review the program each year. |
|
| Practice it | Walk through a realistic incident with your team before it happens. |
|
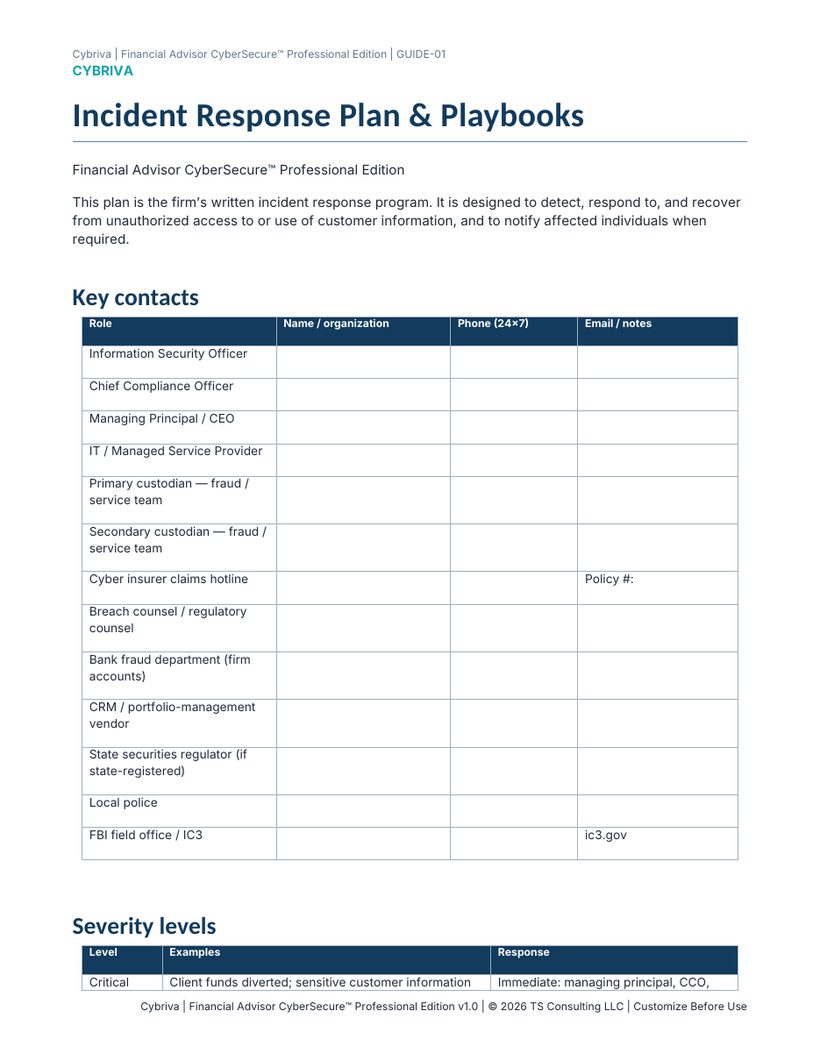
What the Incident Response Plan & Playbooks looks like
Plain-language templates with bracketed fields for your details, policy IDs that stay the same when you upgrade, and a footer reminding you to customize before use.
- Download right after checkout
- Edit in Microsoft Word, Google Docs or any word processor
- One-time price: Starter $149 · Professional $249
Every file in each edition
Policy numbers carry over from the Starter Kit to the Professional Edition, so you can start small and upgrade without renumbering.
Starter Kit
$14924 editable files
Policies 15
- FA-CYB-001Information Security Program & Governance Policy
- FA-CYB-002Risk Assessment & Customer Information Inventory Policy
- FA-CYB-003Access Control & Least Privilege Policy
- FA-CYB-004Multi-Factor Authentication Password Policy
- FA-CYB-005Encryption & Secure Client Communication Policy
- FA-CYB-006Acceptable Use & Workstation Security Policy
- FA-CYB-007Email Security, Phishing & Impersonation Policy
- FA-CYB-008Personnel Security & Confidentiality Policy
- FA-CYB-009Security Awareness & Training Policy
- FA-CYB-010Physical Security & Clean Desk Policy
- FA-CYB-011Backup, Recovery & Business Continuity Policy
- FA-CYB-012Records Retention & Secure Disposal Policy
- FA-CYB-013Service Provider & Custodian Oversight Policy
- FA-CYB-014Incident Response & Customer Notification Policy
- FA-CYB-015Remote Work & Mobile Device Policy
Plans, guides & assessments 8
- WordImplementation Guide
- WordStaff Cybersecurity Quick Guide
- WordIncident Response Plan
- WordWritten Information Security Program (WISP)
- WordClient Security & Money Movement Notice
- Word30-60-90 Day Action Plan
- Word50-Point Cybersecurity Checklist
- WordCybersecurity Maturity Assessment
Workbook 1
- ExcelFinancial Advisor CyberSecure Toolkit
Professional Edition
$24942 editable files
Policies 21
- FA-CYB-001Information Security Program & Governance Policy
- FA-CYB-002Risk Assessment & Customer Information Inventory Policy
- FA-CYB-003Access Control & Least Privilege Policy
- FA-CYB-004Multi-Factor Authentication Password Policy
- FA-CYB-005Encryption & Secure Client Communication Policy
- FA-CYB-006Acceptable Use & Workstation Security Policy
- FA-CYB-007Email Security, Phishing & Impersonation Policy
- FA-CYB-008Personnel Security & Confidentiality Policy
- FA-CYB-009Security Awareness & Training Policy
- FA-CYB-010Physical Security & Clean Desk Policy
- FA-CYB-011Backup, Recovery & Business Continuity Policy
- FA-CYB-012Records Retention & Secure Disposal Policy
- FA-CYB-013Service Provider & Custodian Oversight Policy
- FA-CYB-014Incident Response & Customer Notification Policy
- FA-CYB-015Remote Work & Mobile Device Policy
- FA-CYB-016Identity Theft Red Flags Program Policy
- FA-CYB-017Money Movement & Account Change Verification Policy
- FA-CYB-018Vulnerability Management & Security Testing Policy
- FA-CYB-019Generative AI, Electronic Communications & Cloud Policy
- FA-CYB-020Privacy Notice & Information Sharing Policy
- FA-CYB-021AI Governance Policy
Plans, guides & assessments 10
- WordProfessional Edition Implementation Guide
- WordIncident Response Plan & Playbooks
- WordTabletop Exercise Kit
- Word30-60-90 Day Action Plan
- WordStaff Cybersecurity Quick Guide
- WordWritten Information Security Program (WISP)
- WordClient Security & Money Movement Notice
- Word50-Point Cybersecurity Checklist
- WordCybersecurity Maturity Assessment
- Word50-Question Financial Advisor Cybersecurity Self-Assessment
Forms & templates 10
- FORM-01Money Movement & Account Change Verification Form
- FORM-02Access Request Form
- FORM-03Staff Offboarding Checklist
- FORM-04Software, SaaS & AI Tool Request Form
- FORM-05Security Exception Request
- FORM-06Incident Intake Form
- FORM-07Service Provider Security Questionnaire
- FORM-08Confidentiality Policy Acknowledgment Form
- FORM-09Customer Notification Determination Worksheet
- FORM-10Annual Cybersecurity Review & Management Report
Workbook 1
- ExcelFinancial Advisor CyberSecure Professional Toolkit
Frequently asked questions
When did smaller RIAs have to comply with amended Reg S-P?
June 3, 2026. Larger entities, including RIAs with $1.5 billion or more in assets under management, had to comply by December 3, 2025.
How fast do we have to notify clients?
As soon as practicable, and no later than 30 days after becoming aware that sensitive customer information was, or is reasonably likely to have been, accessed or used without authorization.
Can we decide notice isn't needed?
Yes, if a reasonable investigation finds that substantial harm or inconvenience is not reasonably likely. Document how you reached that conclusion; the kit includes a worksheet for it.
Do we have to change our custodian and vendor contracts?
The rule requires written policies that make service providers protect customer information and notify you within 72 hours. It does not expressly require a contract clause, but many firms add one. Talk to your counsel.
Is this legal or compliance advice?
No. These are editable templates and plain-English education, not a compliance determination. Your CCO and counsel should review them.
Free Financial Advisor cybersecurity self-assessment
Answer 50 yes / no / not sure questions across 10 areas. Score your results and get clear next steps for your industry.
- Small Business, Law Office, Real Estate, Healthcare, Accounting & Tax, Insurance Agency, Financial Advisor, Auto Dealer, Mortgage & Title, and Cyber Insurance Readiness editions
- Starred priority questions and a scoring table
- Printable PDF
Your assessment is ready
Thanks. Your download should start automatically. If it doesn't, use the button below.
Download the PDFQuestions about your results? Email info@cybriva.ai.
Get the Financial Advisor CyberSecure kit
Start with the Starter Kit or get every policy, form and workbook in the Professional Edition. Policy numbers carry over if you upgrade.
See the full Financial Advisor CyberSecure pageSources
- SEC final rule: Regulation S-P amendments (Release 34-100155)
- Davis Wright Tremaine: smaller entities must comply by June 3, 2026
This guide is plain-English education, current as of October 18, 2026. It is not legal advice, an audit or a compliance determination, and Cybriva is not affiliated with any regulator or standards body named here. Rules change and vary by state; confirm how they apply to you with your attorney or compliance advisor.